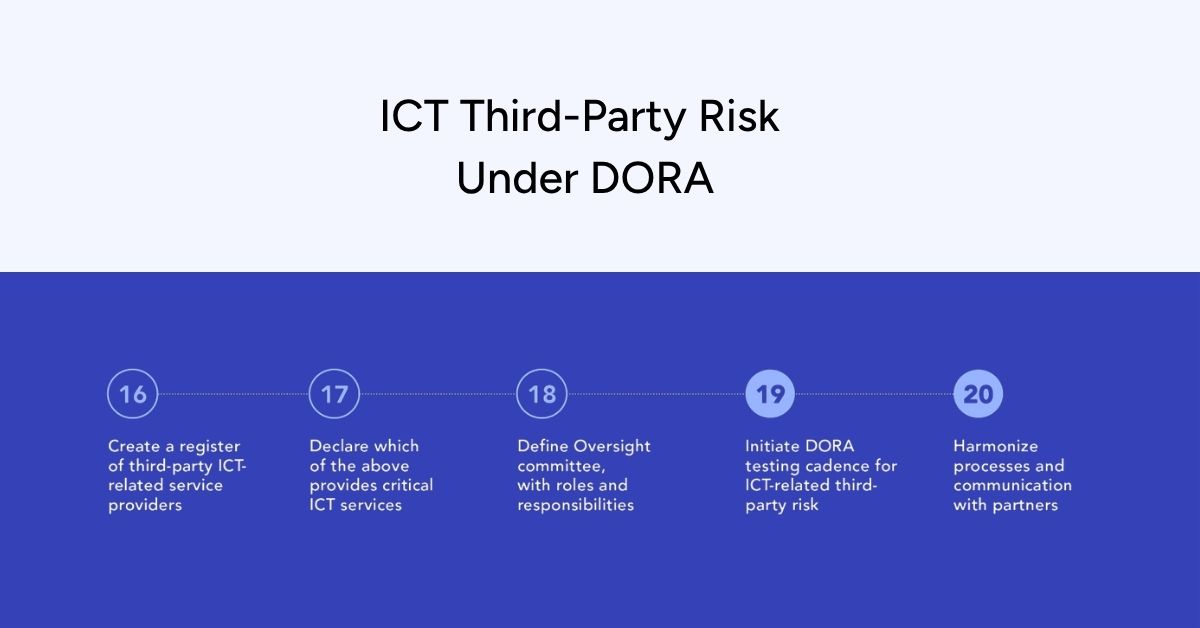
If your organization runs on AWS, Azure, GCP, or any outsourced ICT provider and touches EU financial services, DORA Article 28 is no longer optional reading. It is the article that turns “we outsourced it” from a liability shield into a documentation exercise: financial entities remain fully accountable for every ICT service they buy, and Article 28 […]
If you run technology, security, or infrastructure for a company that touches EU customers, you’ve probably heard both acronyms thrown around interchangeably — they aren’t the same thing. DORA vs NIS2 comes down to one question: are you a regulated financial entity, a critical-infrastructure operator, or, increasingly, both? Getting the answer wrong means either over-building […]
If your organization touches EU financial services — as a bank, insurer, payment provider, crypto-asset firm, or as an ICT vendor selling to any of them — a DORA compliance checklist is no longer optional homework. The Digital Operational Resilience Act (DORA) has been fully in force since January 17, 2025, and 2026 is the year national […]
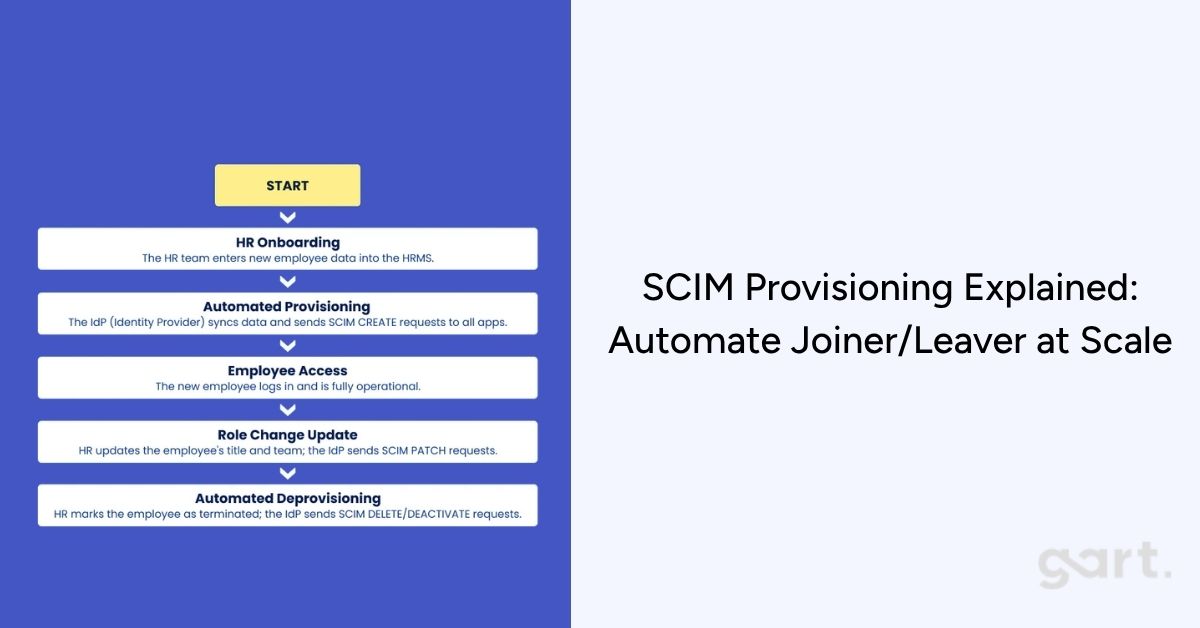
Ask most IT teams how a new hire ends up with working access to Slack, Salesforce, GitHub, and the dozen other tools they need on day one, and the honest answer is still “someone in IT clicks through each app by hand.” SCIM provisioning is the open standard that replaces that manual work with a single, machine-readable […]
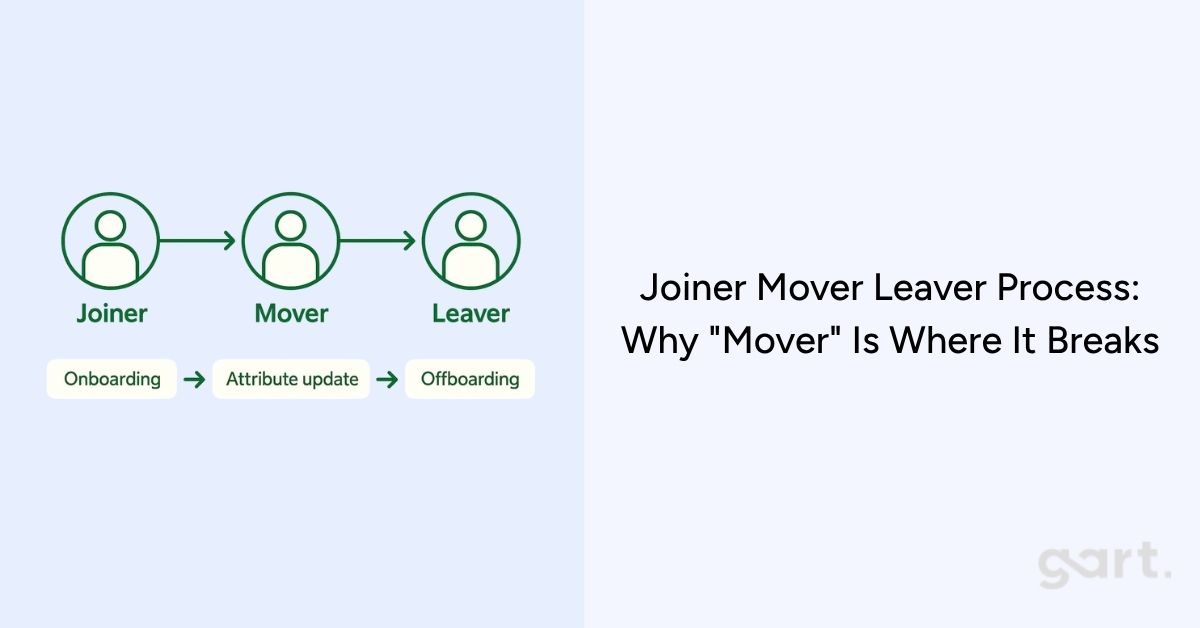
Every company with more than a handful of employees runs some version of the joiner mover leaver process, whether or not anyone calls it that: new hires get accounts, departing employees lose them. What’s far less consistent is the middle step. A joiner-mover-leaver process usually handles the “joiner” and “leaver” ends reasonably well, because both have […]
Every enterprise running Microsoft 365 eventually asks the same question: do we keep certifying access with spreadsheets and email chains, or do we finally turn on Entra ID governance access reviews? The honest answer is more specific than “automate everything.” Most organizations are already paying for a meaningful chunk of Entra ID Governance inside licenses they […]