Client Background
CyberiSight is a leading cybersecurity company specializing in providing comprehensive solutions to individuals and organizations to combat cyber threats. Their services include threat intelligence, vulnerability assessments, incident response, and security consulting.
Challenge
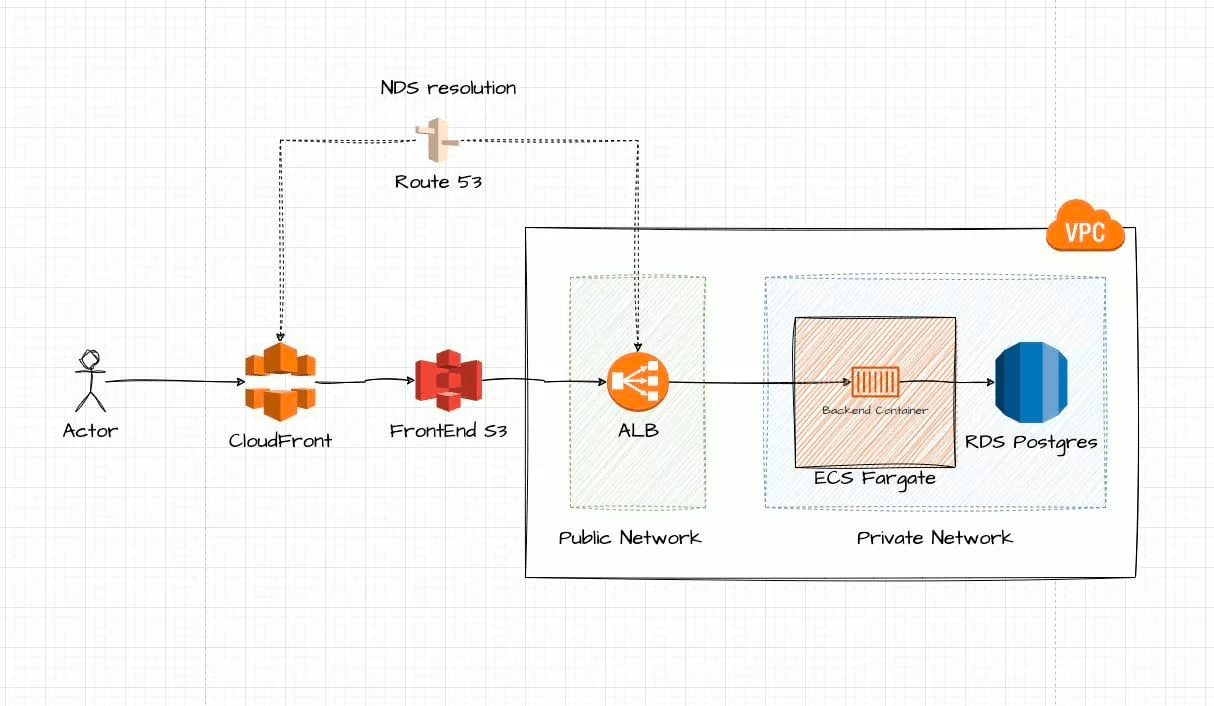
CyberiSight sought to deploy a Node.js and React application to AWS for its cybersecurity product. It needed a CI/CD pipeline using GitLab CI for deployment and Terraform for repeatable infrastructure. It also wanted security tasks into the pipeline, such as dependency checks and application scans, and implement application monitoring solutions.
Solution
After discovering Gart through Upwork, CyberiSight chose us for our exceptional ratings and cost-effectiveness. Our team provided a dedicated member who closely collaborated with CyberiSight to achieve their objectives.
We built a CI/CD pipeline that updates every environment automatically and added automated password rotation with Terraform. The infrastructure was kept simple, with security as the main focus
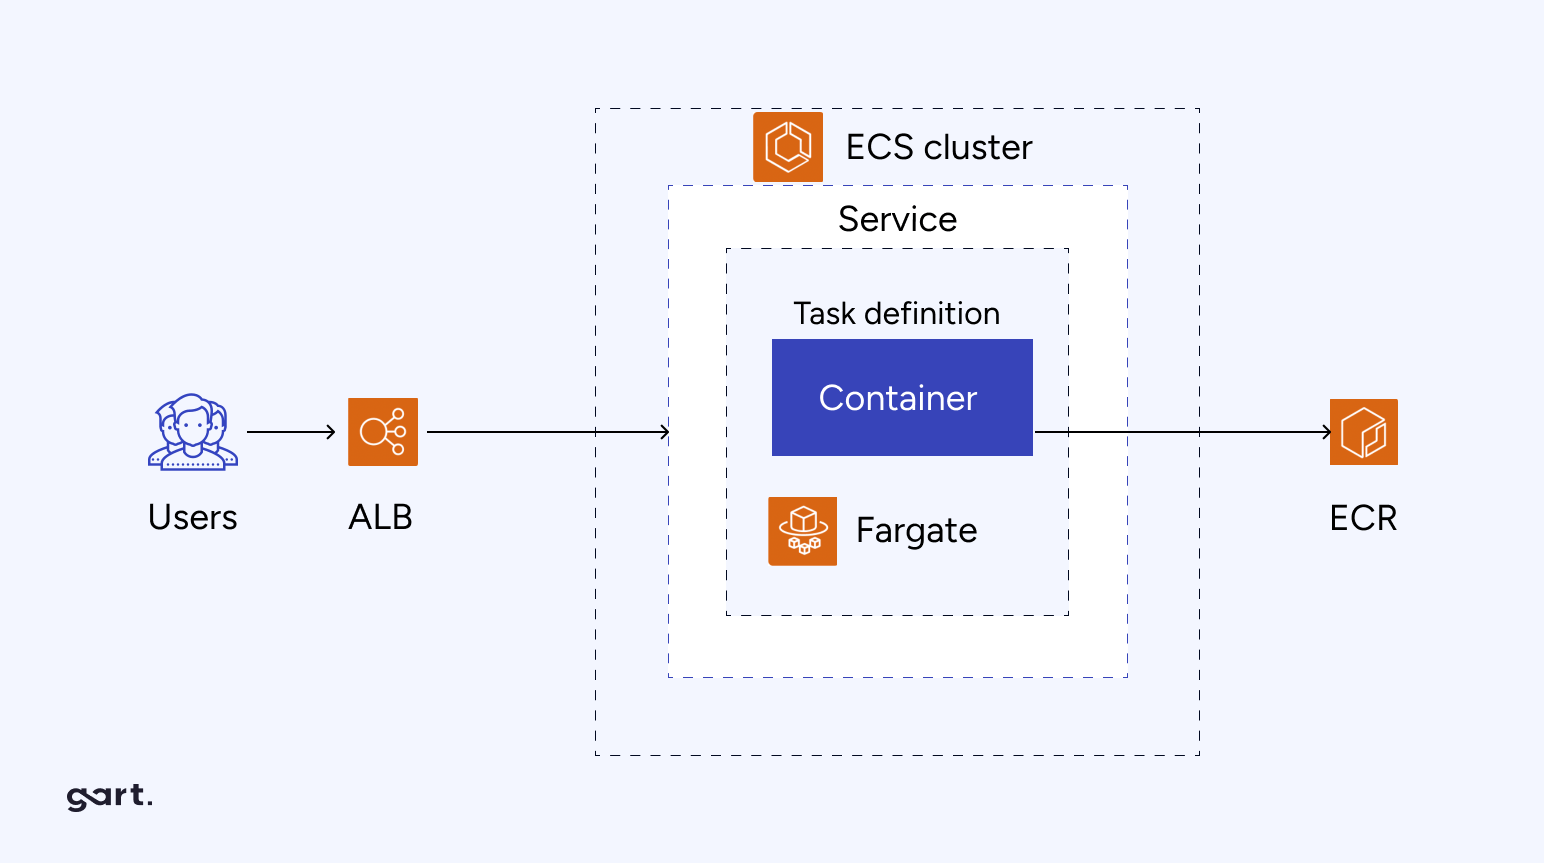
For deploying the Node.js and React application for CyberiSight, we chose AWS ECS (Elastic Container Service), which runs the containers, scales them and handles restarts without a cluster to manage.
Here’s a detailed breakdown of how we effectively deployed with AWS ECS:
Containerization
First, we containerized the Node.js and React applications using Docker. This involved creating Docker images that encapsulated the application code, runtime, dependencies, and configurations.
Setting up ECS Cluster
Next, we created an ECS cluster on AWS. This cluster served as a logical grouping of ECS container instances where our applications would run. We configured the cluster’s capacity and scalability options based on the application’s requirements.
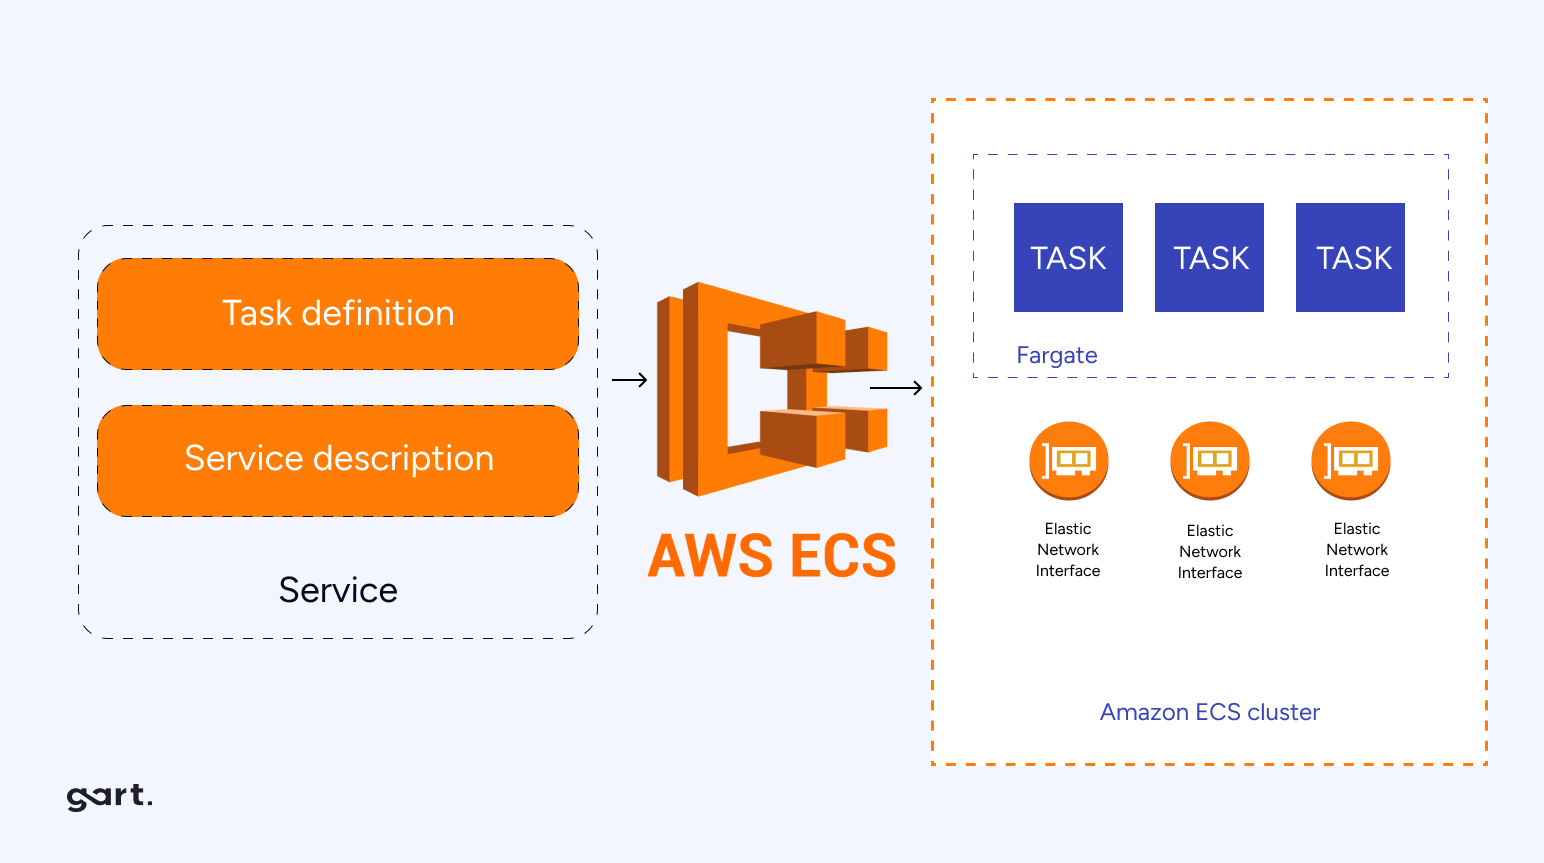
We defined task definitions that described how our containers should be run within the ECS cluster. These task definitions specified parameters such as the Docker image to use, CPU and memory allocations, networking, and storage configurations.
Service Configuration
We configured ECS services to manage and maintain the desired number of tasks based on the application’s requirements. Services ensured that a specified number of tasks were running and automatically handled scaling, load balancing, and fault tolerance.
Deployment
We deployed our Dockerized Node.js and React applications to ECS by creating tasks based on our defined task definitions. ECS automatically scheduled these tasks onto available container instances within the cluster.
Monitoring and Scaling
We utilized AWS CloudWatch and ECS metrics to monitor the performance and health of our deployed applications. We set up alarms to trigger scaling actions based on predefined thresholds, so the service scales out under load and back in when traffic drops.
Continuous Integration and Deployment (CI/CD)
We integrated ECS deployment with our CI/CD pipeline to automate the process of building, testing, and deploying containerized applications. Tools like AWS CodePipeline and AWS CodeBuild streamlined this workflow, allowing for rapid and reliable deployments.