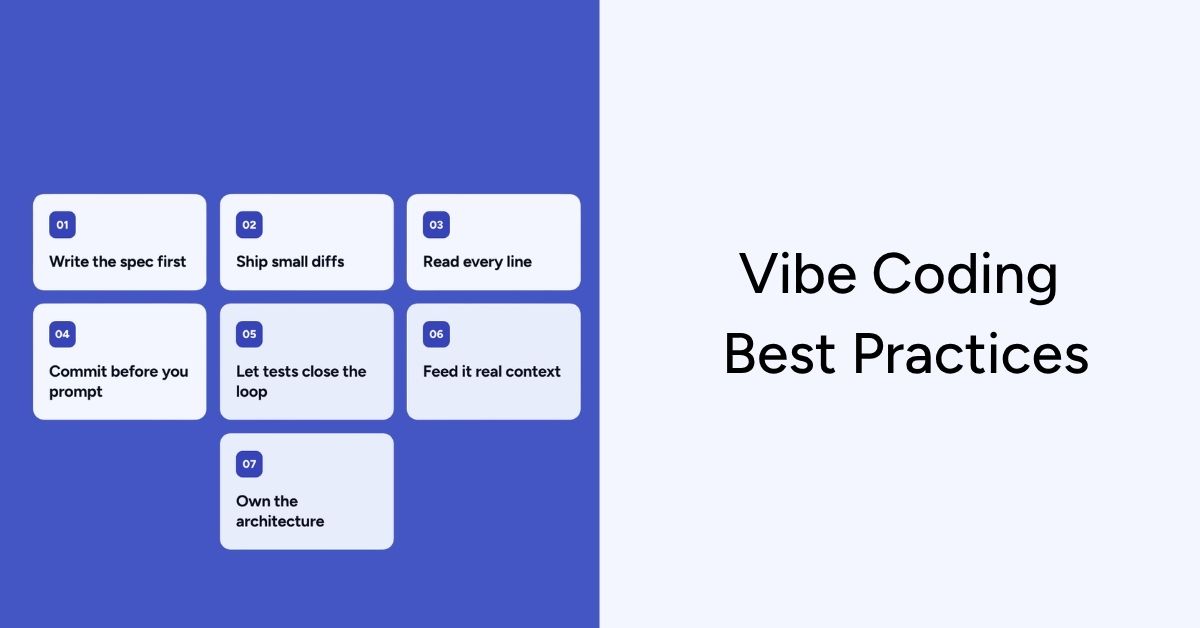
Gartner predicts that by 2028, 40% of new enterprise production software will be built using vibe coding techniques and tools — prompting an AI assistant in natural language rather than hand-writing every line. It's already happening faster than that forecast suggests: by most 2026 estimates, 41-46% of new production code is AI-generated, and Java backends have crossed 61%. The problem isn't the prompting. It's that a working demo and a production-ready application that has passed a real security audit are two very different things, and most teams don't find out which one they've built until it's live and something breaks.
This guide is the vibe coding best practices playbook we actually use when a founder or product team brings us an AI-generated app and asks, "is this safe to launch?" It covers the prompt strategy that gets you closer to production-ready code on the first pass, the security gaps AI assistants reliably leave behind, and the infrastructure checklist — CI/CD, secrets, observability, disaster recovery — that turns a vibe-coded prototype into something Gart's own SRE and DevOps teams would sign off on.
What "vibe coding" actually means in 2026
The term was coined for describing a piece of code by describing what you want in plain English and letting an AI assistant — Claude, Cursor, Lovable, Bolt, Replit, v0, or a dozen similar tools — generate, run, and iterate on it, often with the person driving barely reading the diff. It's no longer a hobbyist curiosity. Stack Overflow's 2025 survey found 84% of developers already use or plan to use AI coding tools, and 63% of self-identified vibe coding users are non-developers: product managers, founders, and designers shipping real, customer-facing software without a traditional engineering background.
That's the upside case. The 2026 data on outcomes is messier. MIT researchers measured a 26% increase in completed tasks across nearly 4,900 developers using AI assistants, and McKinsey found teams saving roughly 3.6 hours a week on routine coding. But a randomized METR study found experienced developers were actually 19% slower on real tasks when using AI tools — while estimating afterward that they'd been 20% faster. Uplevel's research tied Copilot adoption to a 41% increase in bug rates. And separate security research found only 8.25% of one leading model's code outputs were both functionally correct and free of security flaws, with 45% failing OWASP Top 10 benchmarks outright. Vibe coding isn't a shortcut around engineering discipline — it just moves where that discipline needs to be applied: from writing the code to reviewing, securing, and operating it.
Prototype vs. production-ready: the gap in one table
Most of the vibe-coded apps we're asked to review pass this test in under a minute — and that's the point. A weekend prototype and a production system can look identical in the browser while being nothing alike underneath.
DimensionTypical vibe-coded prototypeProduction-ready applicationData access controlDefault-open tables; RLS/authorization added "later"Deny-by-default policies, tested per role before launchSecretsAPI keys pasted into prompts, client code, or .env files committed to gitManaged secrets store with rotation and least-privilege scopingTestingManual click-through by the person who built itAutomated test suite plus an independent review of AI-written logicDeploymentOne environment, deployed by hand from a laptopCI/CD pipeline with staging, rollback, and infrastructure as codeObservabilityNo alerting; issues found when a user complainsMonitoring, error tracking, and on-call escalation pathsDisaster recoveryNo backup strategy beyond the platform's defaultsTested backups, defined RTO/RPO, documented recovery runbookCost controlUnmetered AI-generated queries and autoscaling left uncappedBudget alerts, query review, and right-sized infrastructurePrototype vs. production-ready: the gap in one table
A prompt strategy that produces production-ready code
Most "vibe coding went wrong" stories trace back to a prompt that only described the happy path. AI coding assistants are pattern-matchers trained mostly on demo-quality code; if you don't ask for edge cases, error handling, and security constraints explicitly, you'll rarely get them by default. The prompt strategy that reliably narrows the gap in the table above has three layers, asked in order, not all at once:
Technical context first. State your stack, data model, and architectural constraints before asking for behavior — "PostgreSQL via Supabase, Next.js on Vercel, multi-tenant with row-level isolation by organization_id" — so the assistant isn't guessing at conventions it will contradict three prompts later.
Functional requirements, including the boring parts. Describe the user-facing behavior and explicitly ask for validation, empty states, and error messages, not just the success case.
Integration and edge cases as a direct follow-up. After the first draft, ask: "What could go wrong with this code in production? What edge cases and failure modes am I not handling?" Then ask the model to review its own output "as if this is going live tomorrow" — this single follow-up surfaces missing authorization checks and unhandled errors far more often than a single well-crafted initial prompt does.
Two habits compound this into an actual production-ready-app strategy rather than a one-off trick: ask the assistant to explain why it chose an approach (a model that can't justify a decision usually made a weak one), and treat every AI-generated data access, authentication, or payment code path as a draft that needs a second, human review before merge — never an exception to your normal review process.
Vibe coding security best practices you can't skip
Security is where AI-generated code fails most predictably, and where the consequences are least forgiving. The clearest public example is CVE-2025-48757: a missing Row-Level Security default in Lovable-generated apps that left over 170 live projects — roughly 303 exposed endpoints, CVSS 9.3 — readable and writable by anyone, unauthenticated. It's a textbook case of what breaks when a Lovable + Supabase app reaches production without a security review: the framework defaulted open, and nobody closed it.
Secrets management is the second most common failure mode, and it's getting worse, not better. GitGuardian's 2026 State of Secrets Sprawl report found that AI-assisted commits leak hardcoded secrets at 3.2%, versus a 1.5% baseline across all public GitHub commits — more than double — and secrets tied to AI services specifically grew 81% year over year. Four checks close most of the gap:
Before you ship, verify: row-level security (or equivalent authorization) is enabled and tested for every table and role, not just the default; no API keys or service-role credentials exist in client-side code, prompts, or committed .env files; secrets live in a managed store with rotation, not hardcoded — see our comparison of Kubernetes secrets management approaches if you're deploying on containers; and every AI-generated database and API layer has been checked against production hardening best practices for your specific backend, not just the framework's happy-path defaults.
None of this means AI-generated code is uniquely unsafe — it means it inherits the same risks as any code written under time pressure by someone optimizing for "it works," and vibe coding compresses that pressure into minutes instead of sprints. Building checks like role-based access control directly into the CI/CD pipeline, rather than relying on someone remembering to run them, is what closes the gap for good.
Testing and review discipline for AI-generated code
The trust gap tells you most of what you need to know here: only around 29% of developers say they trust AI-generated code's accuracy, down from roughly 40% two years ago — yet only 48% say they always review AI output before committing it. That mismatch, not the AI itself, is where production incidents come from.
A workable review discipline for vibe-coded code doesn't need to be heavier than normal code review — it needs to target the specific failure modes AI assistants produce: authorization checks that look present but only cover the happy path, error handling that catches the exception but swallows it silently, and logic that's subtly wrong in a way that passes a casual read (research on one frontier model found major-issue rates 1.7x higher than human-written baselines, with logic flaws up 75%). Treat any AI-generated pull request touching auth, payments, or data access as requiring the same second reviewer you'd assign to a junior engineer's first month of commits — because functionally, that's what it is.
The infrastructure checklist before you ship
This is the part that gets skipped most often, because it's invisible right up until it isn't. An app that runs fine on the platform's free tier with ten test users tells you almost nothing about how it behaves under real load, real failure, or a real audit.
CI/CD and infrastructure as code
If deploying means someone pushing a button from their laptop, you don't have a deployment process — you have a single point of failure with a person attached. A proper pipeline with staging, automated tests, and rollback is the single highest-leverage fix available, and it's exactly what our infrastructure-as-code case study walks through for a team that scaled from manual deploys to millions of automated transactions a month.
Observability and reliability
Vibe-coded apps tend to have zero visibility into their own health until a user reports something broken. Basic error tracking, uptime monitoring, and an alerting path aren't optional extras — they're the difference between finding a problem in minutes and finding it in a support ticket three days later. Our breakdown of SRE versus DevOps covers which discipline actually owns this once you're past the prototype stage.
A platform, not a pile of scripts
Teams that vibe-code several apps in parallel — which is increasingly common among the 16 million or so citizen developers now shipping software — run into a second-order problem: every app has its own ad hoc deployment, secrets handling, and monitoring setup. Platform engineering exists to turn that sprawl into a self-service golden path, so the next AI-generated app inherits guardrails instead of starting from zero.
Scale and cost control
AI-generated queries are notorious for missing indexes and doing more database round-trips than a human would write by hand — fine at ten users, expensive and slow at ten thousand. Cap autoscaling, set budget alerts, and load-test before a launch gets real traffic, not after.
When to bring in infrastructure and DevOps help
Not every vibe-coded app needs an outside team — a genuine side project with no user data at stake can stay a weekend project. The signal to act is any combination of: real user data flowing through the app, revenue depending on uptime, a compliance requirement (HIPAA, PCI DSS, SOC 2, GDPR) on the horizon, or a founder realizing they can describe what the app does but not how it fails. At that point, the fastest path isn't rebuilding from scratch — a fractional CTO engagement can sequence exactly which of the fixes in this article matter first for your specific app, before committing to a full rebuild that may not be necessary at all.
Turn your vibe-coded MVP into infrastructure that scales
From a one-time production-readiness audit to full-time DevOps and SRE support, Gart closes the gap between "it works in the demo" and "it survives real traffic" — without a full rebuild.
Security audit
Infrastructure audit
Platform engineering
Cloud migration
CTO as a Service
Get a production-readiness review
You might also like
DevSecOps vs. DevOps: how secure software delivery evolved
What is DevSecOps consulting?
Software reliability through DevOps and SRE
How to hire DevOps engineers that actually move the needle
Roman Burdiuzha
Co-founder & CTO, Gart Solutions · Cloud Architecture Expert
Roman has 15+ years of experience in DevOps and cloud architecture, with prior leadership roles at SoftServe and lifecell Ukraine. He co-founded Gart Solutions, where he leads cloud transformation and infrastructure modernization engagements across Europe and North America. In one recent client engagement, Gart reduced infrastructure waste by 38% through consolidating idle resources and introducing usage-aware automation. Read more on Startup Weekly.
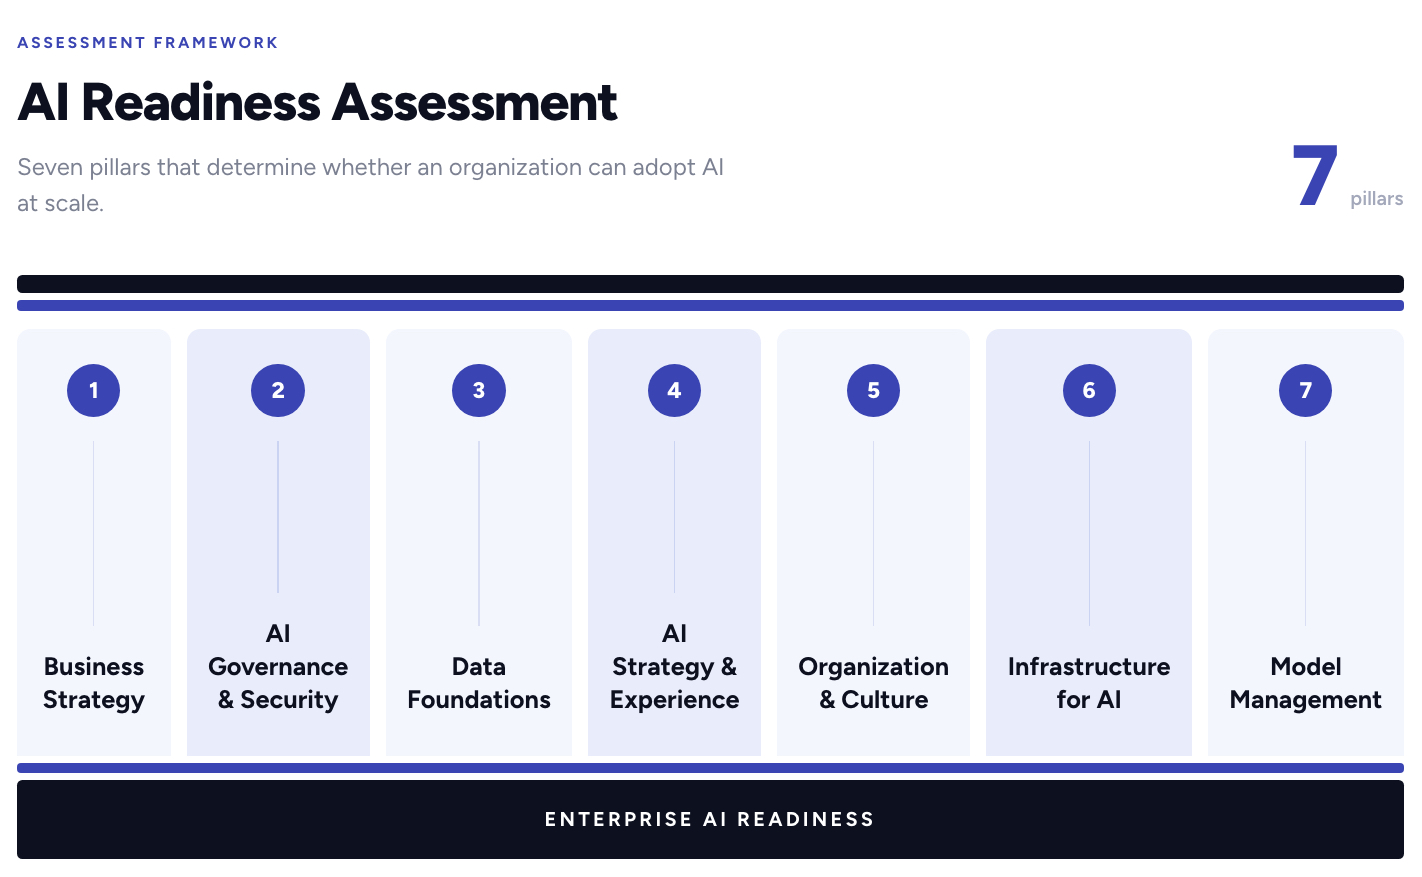
Most companies do not fail at AI because the technology does not work. They fail because no one ran an AI readiness assessment before the budget was approved. An AI readiness assessment is a structured way to find out, pillar by pillar, whether your organization can actually plan, govern, and scale AI — rather than discovering the gaps after a six-figure pilot quietly stalls. This guide walks through the seven pillars that matter most, explains how to score each one honestly, and includes a free, interactive AI readiness assessment you can complete in about 15 minutes. If what it surfaces points to a broader gap than a single team can close alone, that is exactly the kind of work our digital transformation consulting team helps organizations work through.
What is an AI readiness assessment?
An AI readiness assessment is a structured evaluation — usually a scored questionnaire — that measures how prepared an organization is to plan, govern, and scale AI initiatives. It goes beyond asking whether you have used a chatbot or piloted a model. A properly built assessment looks at whether strategy, data, governance, culture, infrastructure, and operational discipline are all mature enough to support AI at scale, not just in a sandbox.
Done well, it works best as a shared exercise rather than a solo one:
Someone who owns technology strategy — a CIO, CTO, or Head of Digital Transformation — to answer the Business Strategy and AI Strategy & Experience questions honestly.
Someone close to data and infrastructure — a data lead or infrastructure architect — for the Data Foundations, Infrastructure for AI, and Model Management pillars.
Someone accountable for risk — security, legal, or compliance — for AI Governance & Security.
Someone representing the rest of the organization — an HR or operations lead — for Organization & Culture.
Completing the assessment from a single vantage point, IT alone especially, tends to overstate readiness on the pillars that person is furthest from.
Why AI readiness matters right now
The gap between AI ambition and AI readiness is well documented, and it is measured in real project failures, not just survey sentiment. Gartner has found that 63% of organizations either do not have or are unsure if they have the right data management practices for AI, and predicts that through 2026, organizations will abandon 60% of AI projects unsupported by AI-ready data. Separate research from Cloudera and Harvard Business Review Analytic Services found that only 7% of enterprises say their data is completely ready for AI.
Those numbers point squarely at Data Foundations, but the same pattern shows up across every pillar in this assessment: organizations invest in AI tooling before they have the strategy, governance, culture, infrastructure, or model management practices to support it. A structured AI readiness assessment exists specifically to surface which of those pillars is the actual bottleneck, rather than guessing.
The 7 pillars of AI readiness
This assessment scores seven pillars independently, because an organization can be strong in one — infrastructure is a common example — while still being genuinely unready in another, such as governance or culture. Each pillar below links to the specific area of Gart's own work most relevant to closing that particular gap.
1. Business Strategy
Business Strategy is the pillar every other pillar depends on. It asks whether AI investment is tied to a documented strategy with named ownership, a working way to measure ROI, and budget that survives past the pilot stage. Organizations that skip this step tend to end up with a portfolio of disconnected experiments instead of a coherent direction — which is exactly the gap our digital transformation consulting engagements are usually brought in to close.
2. AI Governance & Security
Governance covers the policies, approval workflows, and security controls that keep AI use accountable: who reviews a new use case before it ships, how you defend against AI-specific threats like prompt injection, and whether you can demonstrate compliance under frameworks like the NIST AI Risk Management Framework. Regulatory pressure is not theoretical: as of August 2026, Article 50 transparency obligations under the EU AI Act apply to any organization deploying AI systems that interact with people, even though the Act's separate high-risk system obligations have since been deferred. Access control specifically — knowing who and what can reach your AI systems and data — is one of the fastest wins here; see our guide to the least-privilege access model for a practical starting point, or have our team run a full AI compliance audit to see exactly where you stand.
3. Data Foundations
No AI initiative outperforms the data underneath it. This pillar covers data quality, centralization, governance, lineage, and the privacy controls around whatever your models actually train or run on. It is consistently the pillar organizations underestimate the most — and, per the Gartner research cited above, the one most likely to quietly kill an AI project after the budget has already been spent. If your data still lives across disconnected systems, our database migration services are usually the first practical step.
4. AI Strategy & Experience
This pillar measures something strategy documents cannot capture: real, hands-on experience shipping AI-powered features, evaluating vendors, and iterating based on user feedback. Organizations with one AI use case fully in production, measured against clear benchmarks, are consistently better positioned than organizations juggling ten disconnected pilots. If infrastructure is what is holding your pilots back from reaching production, our AI infrastructure readiness assessment goes deeper on that specific gap.
5. Organization & Culture
Even a well-funded, well-governed AI strategy fails if the people expected to use it are not trained, supported, or honestly informed about how it changes their work. This pillar looks at training programs, internal champions or a center of excellence, cross-functional collaboration, and whether experimentation is genuinely encouraged rather than quietly punished when a pilot fails. Change of this kind is usually a leadership problem before it is a technology one — which is exactly where a fractional CTO engagement can help provide the sustained leadership bandwidth many mid-market teams do not have in-house.
6. Infrastructure for AI
Infrastructure for AI asks whether your compute, network, and cloud architecture can actually carry AI workloads at scale: elastic GPU or accelerated compute capacity, latency and throughput tuned for AI pipelines, integration with the rest of your IT environment, and, critically, whether you can see AI-related cloud costs before they surprise you. Cost visibility in particular is where we see the most avoidable pain — our own FinOps and cloud cost management work covers exactly this problem, AI workloads included.
7. Model Management
The final pillar is operational discipline for the models themselves once they are live: monitoring for performance drift, version control and rollback, tracking third-party model deprecations, scheduled retraining, documentation, and an actual plan for retiring a model that no longer earns its keep. This is squarely AIOps territory — see our breakdown of AIOps consulting companies for how this discipline is typically delivered as a managed practice.
Take the free AI readiness assessment
The tool below covers all seven pillars with 49 questions in total — seven per pillar — modeled on the depth of frameworks like Cisco's AI Readiness Index, but scoped for a mid-market or enterprise team to complete in one sitting. It takes about 12 to 18 minutes.
What you get at the end:
An overall AI readiness score and maturity tier, from AI Foundational through AI Leading.
A pillar-by-pillar breakdown showing exactly where you are strongest and weakest.
Tailored, specific recommendations for your lowest-scoring pillars — not generic advice.
How we score your AI readiness
Each of the 49 questions is scored on a 0-to-4 scale, where 4 reflects a mature, embedded practice and 0 reflects no practice in place. Scores within each pillar are summed and converted to a percentage, and your overall AI readiness score is the average across all seven pillars, weighted equally — no single pillar can inflate or hide behind the others. That overall percentage maps to one of five maturity tiers:
0–20%: AI Foundational — just starting.
21–40%: AI Aware — early exploration.
41–60%: AI Developing — real building blocks, clear gaps.
61–80%: AI Advanced — scaling with discipline.
81–100%: AI Leading — enterprise-grade maturity.
The same 0–100% scale applies to each individual pillar, so you can see at a glance whether a low overall score is spread evenly across the business or concentrated in one or two fixable gaps.
Common AI readiness gaps we see
Across the assessments we run with clients, a handful of gaps show up repeatedly in each pillar. None of them are unusual, and none of them are permanent.
PillarCommon gapQuick winBusiness StrategyAI spend is spread across pilots with no named owner or ROI metricAssign one accountable owner and define two measurable outcomes before funding the next initiativeAI Governance & SecurityNo formal review before a new AI use case goes liveStand up a lightweight, risk-based approval step — even a one-page checklist beats noneData FoundationsData needed for AI sits in disconnected, undocumented systemsDocument lineage for your three most AI-critical data sources first, not all of them at onceAI Strategy & ExperienceMultiple pilots running, none reaching productionPick one use case and define launch benchmarks before starting a secondOrganization & CultureAdoption depends on a handful of enthusiastic individualsFormalize an internal AI champion network so knowledge does not walk out the doorInfrastructure for AIAI cloud and GPU costs are tracked after the fact, not monitored proactivelyPut cost alerting in place before scaling any workload past pilot volumeModel ManagementNo monitoring for model drift after deploymentAdd automated drift alerts to your highest-traffic model firstCommon AI readiness gaps we see
You might also like
Top AI Infrastructure Companies in 2026: The Complete Guide
IT Infrastructure Audit Checklist
Digital Sovereignty of Europe: What It Means for Your Cloud Strategy
Fedir Kompaniiets
Co-founder & CEO, Gart Solutions · Cloud Architect & DevOps Consultant
Fedir is a technology enthusiast with over a decade of diverse industry experience. He co-founded Gart Solutions to address complex tech challenges related to Digital Transformation, helping businesses focus on what matters most — scaling. Fedir is committed to driving sustainable IT transformation, helping SMBs innovate, plan future growth, and navigate the "tech madness" through expert DevOps and Cloud managed services. Connect on LinkedIn.
The EU's NIS2 compliance deadline — October 17, 2024 — has come and gone, but the compliance work it triggered hasn't. Most member states have now transposed the directive into national law, registration windows have opened and closed, and 2026 is widely described as the year supervisory authorities move from guidance to active enforcement. Yet only 16% of businesses in scope say they're confident they're fully compliant. If your organization is still treating NIS2 as a deadline you either hit or missed, this guide walks through where enforcement actually stands in 2026, what's changed since the original rollout, and how to close the gap — including where a compliance audit fits into getting there.
The short version: NIS2's transposition deadline passed in October 2024, but national implementation has rolled out unevenly since — Germany's registration window closed July 31, 2026, the Netherlands enters full enforcement mid-2026, and Spain and France are still finalizing their national rules. The European Commission proposed further amendments to the directive in January 2026, and the adjacent Cyber Resilience Act adds its own reporting obligations starting September 11, 2026. NIS2 isn't a deadline you missed or made — it's an ongoing compliance posture regulators are now actively checking.
Where NIS2 Stands in 2026: From Deadline to Enforcement
NIS2 (the updated Network and Information Security Directive) was due to be transposed into the national law of all 27 EU member states by October 17, 2024. That date marked a legal deadline for governments to pass implementing legislation — not a single EU-wide date on which every covered business suddenly became compliant. In practice, transposition and enforcement have rolled out unevenly ever since:
Member state / groupStatus as of 2026Most of the EU (~22–24 of 27 states)Transposed into national law, with implementing legislation and competent authorities in placeGermanyAmended BSI Act in force since December 6, 2025; registration deadline extended once to July 31, 2026 — now closed. Late registration still carries its own fine of up to €500,000, separate from substantive-violation finesNetherlandsLaw enacted, with a staggered entry into full enforcement around mid-2026SpainStill in active legislative process; remains under the older NIS1-based Royal Decree 43/2021 regime pending completion, expected late 2026FranceTransposition act adopted; implementing decrees still being finalized
Adding to the moving target: the European Commission proposed targeted amendments to NIS2 in January 2026 as part of a broader EU cybersecurity package. The proposal would adjust the directive's scope — bringing submarine data-cable infrastructure operators in, taking chemical distributors out (manufacturers stay in scope), adding a requirement to disclose whether a ransom was demanded and paid after a significant ransomware incident, and expanding which companies must appoint an EU representative. None of this is finalized, but it underlines the point: NIS2 compliance in 2026 means tracking a directive that's still being tuned, not checking a box against a document that hasn't changed since 2024. Germany's BSI, for instance, publishes its own running guidance on which organizations must register under the national implementation — worth checking directly if you operate there, since the detail changes as the rules get finalized.
Whatever stage your country is at, the underlying obligation hasn't changed — businesses in scope need their digital infrastructure and data management practices to be secure, resilient, and adaptable to evolving threats, backed by evidence a regulator can actually review. For the official legal text, see Directive (EU) 2022/2555 on EUR-Lex.
Why NIS2 Still Matters for European Businesses
The case for NIS2 was never really about the October 2024 date — it's about the threat environment the directive was built to address, which has kept getting worse, not better. According to ENISA's Threat Landscape 2025 report, which analyzed 4,875 incidents across the EU between July 2024 and June 2025, public administration was the single most targeted sector at 38% of incidents, ransomware activity fragmented across 82 distinct variants rather than concentrating on a few dominant groups, and AI-enabled phishing made up more than 80% of observed social-engineering activity by early 2025.
That 16% figure comes from a survey of 670 business leaders across the UK, Poland, the Netherlands, Ireland, France, Germany, Denmark, and Belgium — and 11% of respondents said they were still unsure whether NIS2 even applied to their organization. That's the real 2026 story: not a deadline that already happened, but a compliance gap most businesses in scope still haven't closed, right as supervisory authorities shift from advisory guidance to active audits.
Which Industries Fall Under NIS2
NIS2 significantly broadened the sectoral scope of the original 2016 directive. Businesses now fall into one of two categories — "essential" or "important" entities — spanning sectors including energy, transport, banking, financial market infrastructure, health, drinking water and wastewater, digital infrastructure, ICT service management, public administration, and space, alongside a second tier covering postal and courier services, waste management, chemicals, food, manufacturing, and digital providers. Size thresholds generally apply (roughly 50+ employees or €10M+ turnover for important entities, 250+ employees or €50M+ turnover for essential entities), though certain critical providers are in scope regardless of size.
The practical effect for many businesses is indirect: NIS2 doesn't always name your industry outright, but if you provide hosting, cloud, data-center, or CDN services to a company that is named — or if you're a supplier deep in an essential entity's chain — NIS2 obligations can reach you through that relationship even when you're not separately listed.
NIS2 Fines and Penalties in 2026
The headline fine ceilings set by the directive haven't changed:
Entity typeMaximum fineOther consequencesEssential entitiesUp to €10 million or 2% of global annual turnover, whichever is higherPersonal liability can extend to management for serious non-complianceImportant entitiesUp to €7 million or 1.4% of global annual turnover, whichever is higherSame personal-liability exposure for managementLate registration (example: Germany)Up to €500,000A separate, standalone penalty — distinct from substantive control failures
What's changed is the enforcement posture around those numbers. Member states can set fine ceilings above the directive's floor — Germany does — so multi-country operators should check local caps rather than assuming the EU minimums are the actual worst case. And 2026 is the year several national authorities, including Germany's BSI, have moved from publishing guidance to actively auditing in-scope organizations. No wave of major published fines has landed as of this writing, but the shift from a grace period to active oversight is itself the headline: the deadline for having a compliance program was 2024; the deadline for having a defensible one is now.
NIS2, DORA, and the Cyber Resilience Act: Which Regime Applies
NIS2 no longer sits alone. Two adjacent EU regulations now overlap with it for a growing number of businesses, and 2026 is the year all three become operationally real at once:
RegulationWho it coversKey 2026 developmentNIS2Essential and important entities across critical sectors (energy, health, digital infrastructure, and more)National registration deadlines closing through 2026; supervisory authorities shifting to active enforcementDORAFinancial entities and their critical ICT third partiesFirst real supervisory enforcement cycle underway; Register of Information filings were due March 31, 2026, with incomplete third-party registers flagged as an enforcement priorityCyber Resilience Act (CRA)Manufacturers of products with digital elements sold in the EUVulnerability and incident reporting obligations take effect September 11, 2026 — over a year ahead of the CRA's full application in December 2027
The CRA's new reporting clock is tight: manufacturers must submit an early warning within 24 hours of becoming aware of an actively exploited vulnerability or severe incident, a detailed notification within 72 hours, and a final report once corrective measures are available. For businesses already carrying NIS2 and, in some cases, DORA third-party risk obligations, the practical challenge is that these regimes currently run on parallel reporting tracks with no single consolidated channel — which makes incident-response process design, not just underlying security controls, a genuine 2026 compliance problem in its own right.
How to Prepare for NIS2 Compliance
Whether your organization missed the original 2024 window entirely or has been working toward compliance since, the practical steps in 2026 look like this — or start with a structured self-assessment using our free NIS2 Compliance Checklist:
Confirm your registration status. If your country's national registration deadline has passed and you haven't registered with the competent authority, register now — late registration is typically treated more leniently than continued non-registration, but it isn't free (see Germany's €500,000 late-registration fine above).
Run a current risk assessment against NIS2's actual control requirements — not the 2024 version of your infrastructure, but what's running today.
Build or update your incident-reporting process to handle NIS2's notification timelines alongside any DORA or CRA obligations that apply to the same business, rather than maintaining separate, uncoordinated processes for each.
Review third-party and sub-processor relationships, particularly hosting, cloud, and data-center providers, since NIS2 obligations can reach your organization through those relationships even when you're not separately named in scope.
Get an independent technical read on where you actually stand — a compliance audit verifies the infrastructure behind your evidence, not just whether a policy document exists.
A few mistakes show up repeatedly in NIS2 readiness work:
Assuming the October 2024 deadline means the work is done. Transposition is a legal starting gun, not a finish line — enforcement is still ramping up in 2026.
Treating NIS2, DORA, and the CRA as separate projects when a business is in scope of more than one — the underlying security-control evidence overlaps significantly, and building one coordinated program is far more efficient than three parallel ones.
Skipping the registration step because the underlying security work feels more urgent — registration is a distinct, time-bound legal obligation with its own penalty, separate from your actual control maturity.
Not accounting for the moving target. With the Commission's January 2026 amendment proposal still working through the legislative process, scope and reporting requirements may shift again before the current cycle settles.
Organizations without an in-house compliance function often route this work through a managed partner rather than building it internally — see our guide to Compliance as a Service for MSPs for how that model works. Teams that want a more ISO 27001-aligned path into NIS2 readiness can also see our NIS2 compliance solution overview.
Choosing an EU Cloud Provider for NIS2 Compliance
Many businesses are consolidating data operations within the EU specifically to simplify NIS2 compliance and reduce their reliance on sub-processors outside Europe — fewer cross-border data flows to document, fewer third-party relationships to monitor, and a shorter chain between your infrastructure and the regulator's actual jurisdiction. When evaluating a provider against NIS2 requirements, prioritize transparent data-processing locations, minimal reliance on further sub-processors, a demonstrable compliance track record, and clear contractual commitments to EU-based data handling. For a deeper look at what that evaluation actually involves, see our guide to choosing an EU cloud provider.
Also, Gart Solutions, together with our partner — vBoxx, a renowned EU cloud solutions provider, offers a range of managed hosting and cloud server services that can significantly support businesses in their digital transformation journey.
1. Understanding the NIS2 Directive
The NIS2 Directive represents a significant evolution in EU cybersecurity regulation, broadening the scope of compliance requirements to include a wider array of sectors. This directive underscores the necessity of not only securing data but also understanding its entire journey.
Organizations must be vigilant about tracking their data flow to mitigate risks and meet the stringent new standards imposed by NIS2.
2. Comprehensive Data Tracking
Compliance with NIS2 requires an in-depth understanding of where and how data is processed, stored, and transferred. This involves documentation of every stage of the data lifecycle — from creation and processing to storage and eventual deletion. By mapping out the data journey, organizations can better identify vulnerabilities and ensure that all parties involved in data handling adhere to high security standards.
3. The Challenge of Sub-processors
One of the most complex challenges introduced by NIS2 is the need for organizations to maintain visibility over all sub-processors involved in data processing. Each sub-processor, regardless of their role, must meet the same rigorous cybersecurity standards. This requires thorough vetting and ongoing monitoring to ensure compliance, making it critical for businesses to establish strong relationships and clear communication channels with their sub-processors.
4. Strategic Shifts in the Market
In response to NIS2, many businesses are re-evaluating their reliance on third-party sub-processors, especially those located outside the EU. By consolidating data operations within the EU, organizations can better manage compliance and reduce the risk of data breaches.
This trend towards localized data handling is reshaping the market, as companies seek to simplify their data ecosystems and enhance security.
5. Practical Steps for Compliance
To align with NIS2, businesses must take proactive measures, such as engaging closely with their service providers, conducting comprehensive risk assessments, and considering a shift to EU-based data centers and services. These steps not only facilitate compliance but also strengthen the overall cybersecurity posture, ensuring that the organization is well-prepared to meet current and future regulatory demands.
How Not to Repeat Mistakes: Case of Microsoft
If you say, we are using public data providers, there’s still are pitfalls we have to consider.
Let’s take, for example, Microsoft. Microsoft's products continue to be widely used, but they present significant challenges in transparency and data security.
At the time of writing, Microsoft lists 47 subprocessors and 36 data centers, but details on their operations and data handling are unclear. This is concerning given Microsoft's ongoing GDPR violations and multiple security breaches last year.
Moreover, the global spread of subprocessors, often linked to parent companies in various countries, adds complexity and potential security risks, making it difficult for companies to verify compliance and data safety.
Final words
Prepare your business for the NIS2 compliance update with the expert guidance of Gart Solutions. Download our Free Checklist — a comprehensive guide to the NIS2 audit, and ensure your organization is ready for the upcoming changes.
NIS2-Compliance-Checklist-A-Comprehensive-Guide-to-Audit_Free-PDFDownload
Wanna know how? Contact us.
Schedule a Free Consultation
See how we can help to overcome the challenges of NIS2 compliance.
Contact us
You might also like
GDPR Compliance Checklist: What Compliance Automation Can (and Can't) Do
Why ISO 27001 Is a Crucial Step for Successful Companies
Compliance Monitoring: Ensuring Businesses Stay on the Right Side
SOC 2 Compliance: A Step-by-Step Guide to Preparing for Your Audit
PCI DSS Audit Preparation: A Step-by-Step Compliance Guide